ForensicDbg
A modern postmortem debugger for tracing the causes of native Windows crashes
 SITE CAPTURE
Based on information published on the service's website. Selection and review policy
WHAT IT DOES
What does it do?
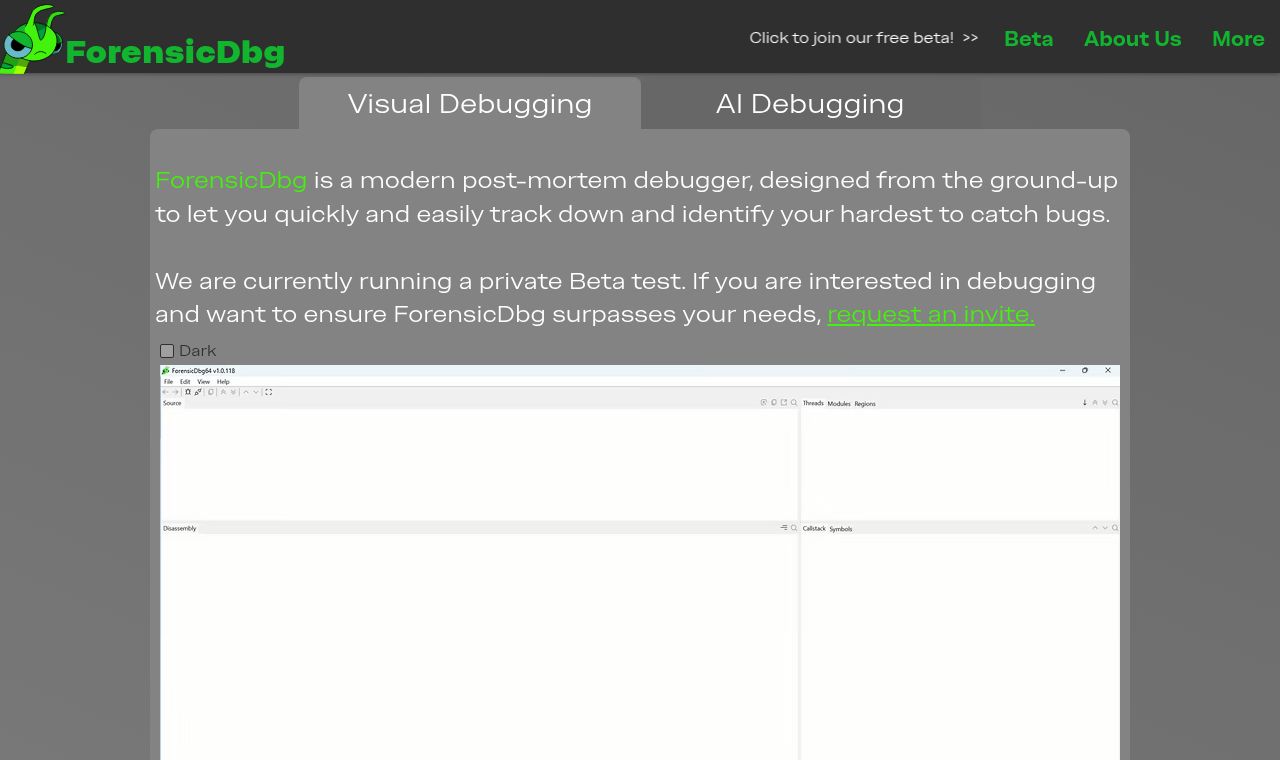
ForensicDbg is an advanced user-mode postmortem debugger for Windows. It analyzes x86 and x64 crash dumps and attaches to running processes. It supports just-in-time debugging, a C++ expression evaluator, SourceServer, and SourceLink. Through a stdio MCP interface, it provides processed output that AI tools can use for crash analysis.
KEY FEATURES
Key features
- Debug x86 and x64 crash dumps
- Attach to running processes
- Set it as a just-in-time debugger that runs when a crash occurs
- Evaluate simple C++ expressions
- Support SourceServer and SourceLink
- Automated AI crash analysis through stdio MCP