
is-malicious
A scanner that points out suspicious files and lines before you run unfamiliar code
 SITE CAPTURE
Based on information published on the service's website. Selection and review policy
WHAT IT DOES
What does it do?
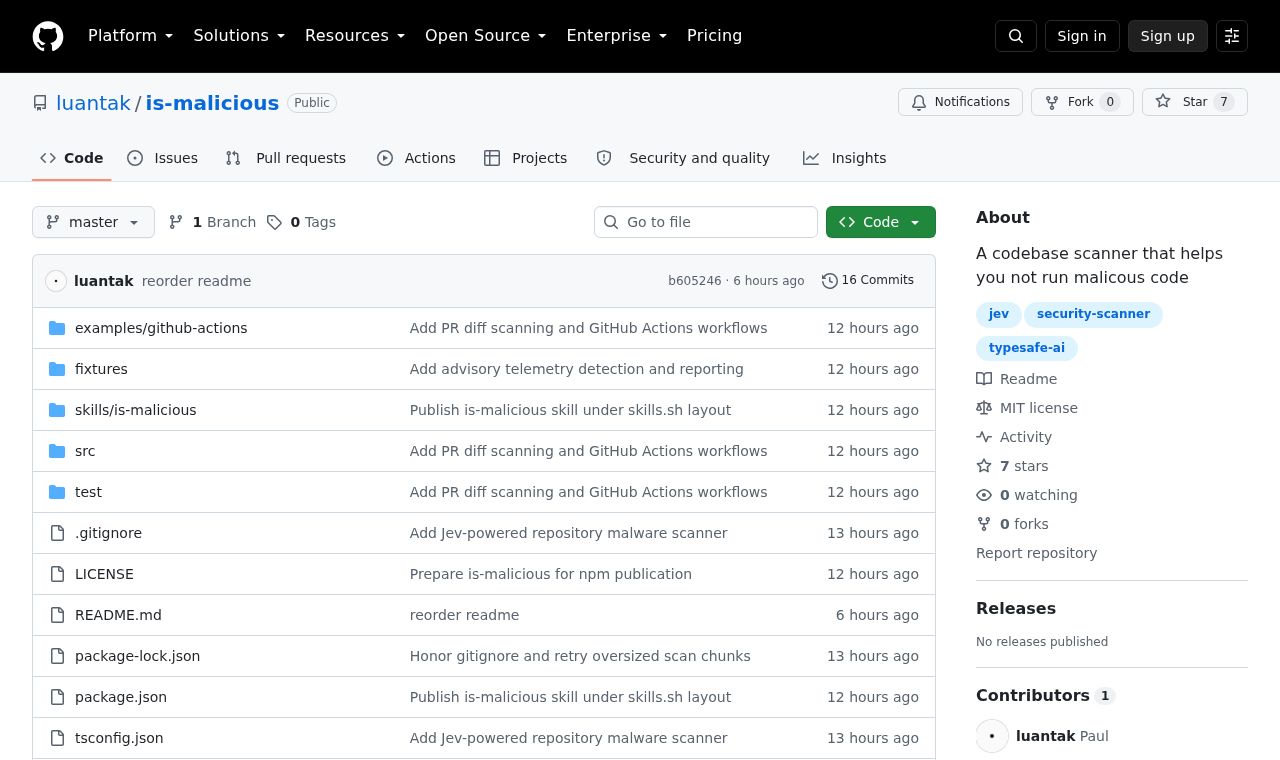
is-malicious is a TypeSafe Jev-based scanner that offers a second opinion before you run unfamiliar code. Findings include the file, line range, category, probability, confidence, and a brief reason. It does not scan binaries, running processes, known dependency vulnerabilities, or committed secrets, and it does not sandbox code.
KEY FEATURES
Key features
- Scan source, configuration, build, and CI files for suspicious behavior
- Identify suspicious files and line locations
- Report findings with categories, probabilities, confidence, and reasons
- Show documented telemetry as separate information
- Respect gitignore and scan only selected text files
- Support workflows that scan changed files in pull requests